• Thanks for stopping by. Logging in to a registered account will remove all generic ads. Please reach out with any questions or concerns.

Hybrid Warfare and Sabotage

Here is an interesting article.

"The clandestine world’s new reality
High-quality photos of military installations or convoys. Acts of sabotage against military equipment. Arson attacks on factories building military hardware or warehouses with supplies for Ukraine. Threats and physical violence against activists or CEOs of defense contractors. In the past, like the Cold war, such acts would have been carried out by highly trained intelligence officers or spies. Massive, highly coordinated spy rings run by intelligence officers and diplomats residing in a hostile country. That is how various intelligence agencies, particularly the Soviet KGB (later, Russian Federal security bureau, FSB) have been running their operations for decades. It required enormous resources, physical presence, personalized recruitment, and risky covert action. Not to mention that in an event that a spy ring is exposed, the state that sent them could face a massive retaliation...."

 
  • Like
Reactions: ytz
Here is an interesting article.

"The clandestine world’s new reality
High-quality photos of military installations or convoys. Acts of sabotage against military equipment. Arson attacks on factories building military hardware or warehouses with supplies for Ukraine. Threats and physical violence against activists or CEOs of defense contractors. In the past, like the Cold war, such acts would have been carried out by highly trained intelligence officers or spies. Massive, highly coordinated spy rings run by intelligence officers and diplomats residing in a hostile country. That is how various intelligence agencies, particularly the Soviet KGB (later, Russian Federal security bureau, FSB) have been running their operations for decades. It required enormous resources, physical presence, personalized recruitment, and risky covert action. Not to mention that in an event that a spy ring is exposed, the state that sent them could face a massive retaliation...."


One route not mentioned.

Civilian servers, both corporate and hobbyist.

They can be gleaned for information but they can also be used to direct operations.

If a directive were issued to an employee from a manager is the employee going to question it? The real manager's accounts could be hacked or the manager could be entirely imaginary.

Likewise suggestions from fellow enthusiasts on a hobby account.

And how many of us have received scam calls from Revenue Canada, Service Canada and Canada Post?

A friend of a friend of a friend.
 
One route not mentioned.

Civilian servers, both corporate and hobbyist.

They can be gleaned for information but they can also be used to direct operations.

If a directive were issued to an employee from a manager is the employee going to question it? The real manager's accounts could be hacked or the manager could be entirely imaginary.

Likewise suggestions from fellow enthusiasts on a hobby account.

And how many of us have received scam calls from Revenue Canada, Service Canada and Canada Post?

A friend of a friend of a friend.
We have to move to a tokenized transmission structure so that agnostic verification can be performed automatically without dealing with the contents of the message itself.

A strange consequence of this would be the subsequent mean reversion to highly skilled operators as primary control/contact points. This would be a continuous selection of only the most fit (capable and intelligent) officers. As our narrowing of anonymity increases, all sides are going to undergo an espionage transformation which parallels the post-Cold War (huge conscript armies) to GWOT (special forces) restructuring.

The training cycle for this transformation should already be underway. The easy pickings of sloughable assets is going to come to an abrupt end. Anyone who falls into the complacency trap of 'We can just trick idiots online to do our dirty work' is going to have a brutal reality check. It is of the utmost importance that we do not structure our avenues of approach around open Internet assumptions.

I will refrain from speculating on the Russian's capabilities in this regard. It remains to be seen if anyone in the global IC really appreciates the looming signals vacuum that panopticon AI's will enforce. While this should reduce the low level harassment discussed here, it will not provide genuine strategic intelligence/deterrence. That will always remain a human's sacrifice.

Now is the EU really taking this seriously?
 
We have to move to a tokenized transmission structure so that agnostic verification can be performed automatically without dealing with the contents of the message itself.

A strange consequence of this would be the subsequent mean reversion to highly skilled operators as primary control/contact points. This would be a continuous selection of only the most fit (capable and intelligent) officers. As our narrowing of anonymity increases, all sides are going to undergo an espionage transformation which parallels the post-Cold War (huge conscript armies) to GWOT (special forces) restructuring.

The training cycle for this transformation should already be underway. The easy pickings of sloughable assets is going to come to an abrupt end. Anyone who falls into the complacency trap of 'We can just trick idiots online to do our dirty work' is going to have a brutal reality check. It is of the utmost importance that we do not structure our avenues of approach around open Internet assumptions.

I will refrain from speculating on the Russian's capabilities in this regard. It remains to be seen if anyone in the global IC really appreciates the looming signals vacuum that panopticon AI's will enforce. While this should reduce the low level harassment discussed here, it will not provide genuine strategic intelligence/deterrence. That will always remain a human's sacrifice.

Now is the EU really taking this seriously?
Huh?
 
We have to move to a tokenized transmission structure so that agnostic verification can be performed automatically without dealing with the contents of the message itself.

A strange consequence of this would be the subsequent mean reversion to highly skilled operators as primary control/contact points. This would be a continuous selection of only the most fit (capable and intelligent) officers. As our narrowing of anonymity increases, all sides are going to undergo an espionage transformation which parallels the post-Cold War (huge conscript armies) to GWOT (special forces) restructuring.

The training cycle for this transformation should already be underway. The easy pickings of sloughable assets is going to come to an abrupt end. Anyone who falls into the complacency trap of 'We can just trick idiots online to do our dirty work' is going to have a brutal reality check. It is of the utmost importance that we do not structure our avenues of approach around open Internet assumptions.

I will refrain from speculating on the Russian's capabilities in this regard. It remains to be seen if anyone in the global IC really appreciates the looming signals vacuum that panopticon AI's will enforce. While this should reduce the low level harassment discussed here, it will not provide genuine strategic intelligence/deterrence. That will always remain a human's sacrifice.

Now is the EU really taking this seriously?

Devil's advocacy time:

In doing as you suggest we are doing the enemy's work.

One of Ukraine's great advantages has been its ability to exploit existing comms and open source intelligence. They have greatly shortened their OODA loops as a result and sped up their kill chains.

Recently I posted an article where American tank forces posted that they had successfully operated in a drone rich environment. But close reading suggested that they had lost their traditional advantages of mass and speed. They had been forced to disperse and move at walking speed. In large part they had been neutered.

More layers of security will have the same effect on our C5ISR systems at the exact time that we are trying to make them more efficient.

It is the same problem I have had with my computer. My computer burns more energy, uses more bits, requires reqular updates, is slower and more quirky, largely due to increased security efforts.

The problem is this:

The Chief of Police wants the auditorium foors locked to control traffic.

The Fire Chief wants the doors open to ease movement of traffic.
 
Our civilian infrastructure is being used against us. At the outbreak of hostilities all cross border Internet traffic will stop. It will create a signalling vacuum. Old school methods (micro dots etc) will remain the only viable solution. If we embrace the new models without maintaining capacity for older, proven, methods, we will lose all communication ability with information sources behind enemy lines.

Devil's advocacy time:

In doing as you suggest we are doing the enemy's work.

One of Ukraine's great advantages has been its ability to exploit existing comms and open source intelligence. They have greatly shortened their OODA loops as a result and sped up their kill chains.

Recently I posted an article where American tank forces posted that they had successfully operated in a drone rich environment. But close reading suggested that they had lost their traditional advantages of mass and speed. They had been forced to disperse and move at walking speed. In large part they had been neutered.

More layers of security will have the same effect on our C5ISR systems at the exact time that we are trying to make them more efficient.

It is the same problem I have had with my computer. My computer burns more energy, uses more bits, requires reqular updates, is slower and more quirky, largely due to increased security efforts.

The problem is this:

The Chief of Police wants the auditorium foors locked to control traffic.

The Fire Chief wants the doors open to ease movement of traffic.
I understand and I agree. My comment is directed at intelligence methods which piggy back on civilian signalling systems. Everyone uses the same noise. But when everything goes silent how do we (Canada in particular, NATO as a whole) continue to run information networks across enemy infrastructure (analog - postal services etc. and digital).

A consequence of AI will be the reversion to elite, analog, sources and methods. These take a very long time to build and deploy. If we fall into the trap of letting these skills atrophy we will be blinded day one. The current hybrid war Russia is waging in Europe directly reflects both of these realities. Which is a major point in the article I posted.
 
Our civilian infrastructure is being used against us. At the outbreak of hostilities all cross border Internet traffic will stop. It will create a signalling vacuum. Old school methods (micro dots etc) will remain the only viable solution. If we embrace the new models without maintaining capacity for older, proven, methods, we will lose all communication ability with information sources behind enemy lines.
You are so right. From what I read in CARS I can operate in Canadian airspace IFR with only GPS. Think of the ramifications of that if someone wishes to work havoc on civilian flight? GPS is easily spoofed as Russia does constantly.
 
Our civilian infrastructure is being used against us. At the outbreak of hostilities all cross border Internet traffic will stop. It will create a signalling vacuum. Old school methods (micro dots etc) will remain the only viable solution. If we embrace the new models without maintaining capacity for older, proven, methods, we will lose all communication ability with information sources behind enemy lines.


I understand and I agree. My comment is directed at intelligence methods which piggy back on civilian signalling systems. Everyone uses the same noise. But when everything goes silent how do we (Canada in particular, NATO as a whole) continue to run information networks across enemy infrastructure (analog - postal services etc. and digital).

A consequence of AI will be the reversion to elite, analog, sources and methods. These take a very long time to build and deploy. If we fall into the trap of letting these skills atrophy we will be blinded day one. The current hybrid war Russia is waging in Europe directly reflects both of these realities. Which is a major point in the article I posted.

I am a fan of retaining residual capacity.
 
Our civilian infrastructure is being used against us. At the outbreak of hostilities all cross border Internet traffic will stop. It will create a signalling vacuum. Old school methods (micro dots etc) will remain the only viable solution. If we embrace the new models without maintaining capacity for older, proven, methods, we will lose all communication ability with information sources behind enemy lines.


I understand and I agree. My comment is directed at intelligence methods which piggy back on civilian signalling systems. Everyone uses the same noise. But when everything goes silent how do we (Canada in particular, NATO as a whole) continue to run information networks across enemy infrastructure (analog - postal services etc. and digital).

A consequence of AI will be the reversion to elite, analog, sources and methods. These take a very long time to build and deploy. If we fall into the trap of letting these skills atrophy we will be blinded day one. The current hybrid war Russia is waging in Europe directly reflects both of these realities. Which is a major point in the article I posted.


Regimental numbers and face masks.
 
Our civilian infrastructure is being used against us. At the outbreak of hostilities all cross border Internet traffic will stop.
Unlikely.
It will create a signalling vacuum. Old school methods (micro dots etc) will remain the only viable solution.
You conflate information transmission with information storage in the above comment wrt microdots.
But you are also wrong on transmission aspects.

If we embrace the new models without maintaining capacity for older, proven, methods, we will lose all communication ability with information sources behind enemy lines.
Ah yeah Omni directional analog Morse code for the win
animation collection GIF


I understand and I agree. My comment is directed at intelligence methods which piggy back on civilian signalling systems. Everyone uses the same noise. But when everything goes silent how do we (Canada in particular, NATO as a whole) continue to run information networks across enemy infrastructure (analog - postal services etc. and digital).

A consequence of AI will be the reversion to elite, analog, sources and methods.
Pardon?


These take a very long time to build and deploy. If we fall into the trap of letting these skills atrophy we will be blinded day one.

I will assume you mean HumInt direct source.

The current hybrid war Russia is waging in Europe directly reflects both of these realities. Which is a major point in the article I posted.
The article is garbage.
Nothing Russia is doing is really new, other than they don’t have Bulgarians to do their wet work like they did in the days of the USSR.

Sure the internet has allowed for some easier proxy sourcing, but the main ‘novel’ aspect of Russian activities has been their disinformation campaigns.

Russia for years gathered proxies to use for nefarious activities. They supported pretty much any anarchistic or communist entity in the West to agitate, and more.
 
Unlikely.
You may want to send the Kremlin a nicely worded letter encouraging them to keep it up then.

"We observed the following ASNs being disconnected from the IX:

28 February: AS57629 (LLC IVI.RU), AS42861 (Foton Telecom CJSC)
1 March: AS47626 (Timer, LLC)
8 March: AS57363 (CDNvideo LLC)
11 March: AS8641 (LLC Nauka-Svyaz), AS35598 (Inetcom LLC)
15 March: AS60764 (TK Telecom), AS60388 (Limited Liability Company Transneft Telecom)
As we can see, many Russian networks stopped propagating their routes through the Giganet Exchange in Kiev, therefore breaking the direct connections between Ukrainian networks. It might be that these networks deliberately decided to shut down their BGP peering sessions based on instructions from the Russian authorities.

IXPs play an important role in shortening paths between networks. They help keep local traffic local and reduce latency between networks. Removing peers from an IXP reduces the number of direct routes that can be used to send traffic to other peers and this can have an impact on latency as well as on the actual “cost” of sending traffic."


Just in case you think they are going to play nice and allow us to communicate across their networks.

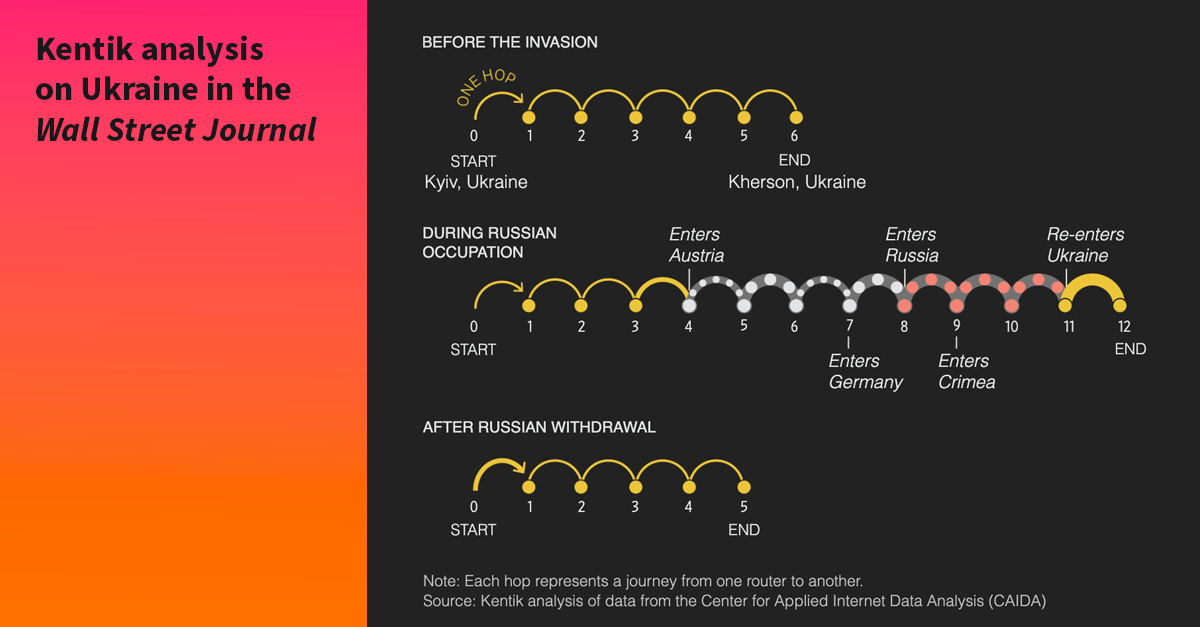
"Arguably the most dramatic development that appears in the data was the rerouting of internet service to Kherson through Russia. To analyze this development, we extracted the traceroutes performed by the Ark server in Kyiv to IP address space originated by the ASes of Kherson."


To simplify my point, and the clear implication of the article I posted, 'they' are burning through the deadwood of our online idiots while conserving their elite human assets for future operations in a signals vacuum environment. We need to ensure our immediate response to their battlespace preparation in western Europe doesn't displace a very necessary long term focus on equivalent talent generation.

Edited to add this link in case you'd like another source.

And their explicit authority:
"On March 1, a new directive will come into effect that grants the Russian Communications Authority (RosKomNadZor) legal means to direct and manage national internet traffic. It will coordinate with providers to maintain functionality in the event of a crisis, interruption, or cyberattack. The decision to take such measures will be made by an interagency committee formed by Russia’s Ministry of Digital Technologies, Communications Authority, and Federal Security Service (FSB) (Official Publication of Legal Acts of Russia, October 27, 2025; GoGovRu, November 18, 2025)."
 
Last edited:
and if they are working within the U.S. it is logical to assume that they are going after Canadian targets as well. But we are OK 'cause we have a shared policing agreement.
 
You may want to send the Kremlin a nicely worded letter encouraging them to keep it up then.

"We observed the following ASNs being disconnected from the IX:

28 February: AS57629 (LLC IVI.RU), AS42861 (Foton Telecom CJSC)
1 March: AS47626 (Timer, LLC)
8 March: AS57363 (CDNvideo LLC)
11 March: AS8641 (LLC Nauka-Svyaz), AS35598 (Inetcom LLC)
15 March: AS60764 (TK Telecom), AS60388 (Limited Liability Company Transneft Telecom)
As we can see, many Russian networks stopped propagating their routes through the Giganet Exchange in Kiev, therefore breaking the direct connections between Ukrainian networks. It might be that these networks deliberately decided to shut down their BGP peering sessions based on instructions from the Russian authorities.

IXPs play an important role in shortening paths between networks. They help keep local traffic local and reduce latency between networks. Removing peers from an IXP reduces the number of direct routes that can be used to send traffic to other peers and this can have an impact on latency as well as on the actual “cost” of sending traffic."

You lost me.
As what I took issue with wasn’t some localized disruption. Because at the end of the day Russia re-routing and isolating parts of occupied Kherson should not be shocking.


You claimed that in the event of hostilities that Cross Border Internet Traffic would stop.
There are a lot of ways to get on the internet.


Just in case you think they are going to play nice and allow us to communicate across their networks.

"Arguably the most dramatic development that appears in the data was the rerouting of internet service to Kherson through Russia. To analyze this development, we extracted the traceroutes performed by the Ark server in Kyiv to IP address space originated by the ASes of Kherson."

Isolated area.

To simplify my point, and the clear implication of the article I posted, 'they' are burning through the deadwood of our online idiots while conserving their elite human assets for future operations in a signals vacuum environment.
I’m legitimately confused what your buzzword salad is supposed to mean.


We need to ensure our immediate response to their battlespace preparation in western Europe doesn't displace a very necessary long term focus on equivalent talent generation.
Just what do you think is missing from
western capabilities?


Edited to add this link in case you'd like another source.

And their explicit authority:
"On March 1, a new directive will come into effect that grants the Russian Communications Authority (RosKomNadZor) legal means to direct and manage national internet traffic. It will coordinate with providers to maintain functionality in the event of a crisis, interruption, or cyberattack. The decision to take such measures will be made by an interagency committee formed by Russia’s Ministry of Digital Technologies, Communications Authority, and Federal Security Service (FSB) (Official Publication of Legal Acts of Russia, October 27, 2025; GoGovRu, November 18, 2025)."
Which helps us actualy.
Nothing will get done / at least that isn’t corruptible.


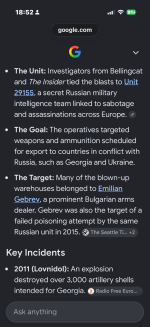
Less than 3 days after the 2011 explosion of the first of the Munitions Storage sites, the leader and the 3 GRU operatives where known to Western Intelligence.

What was done? Nothing.

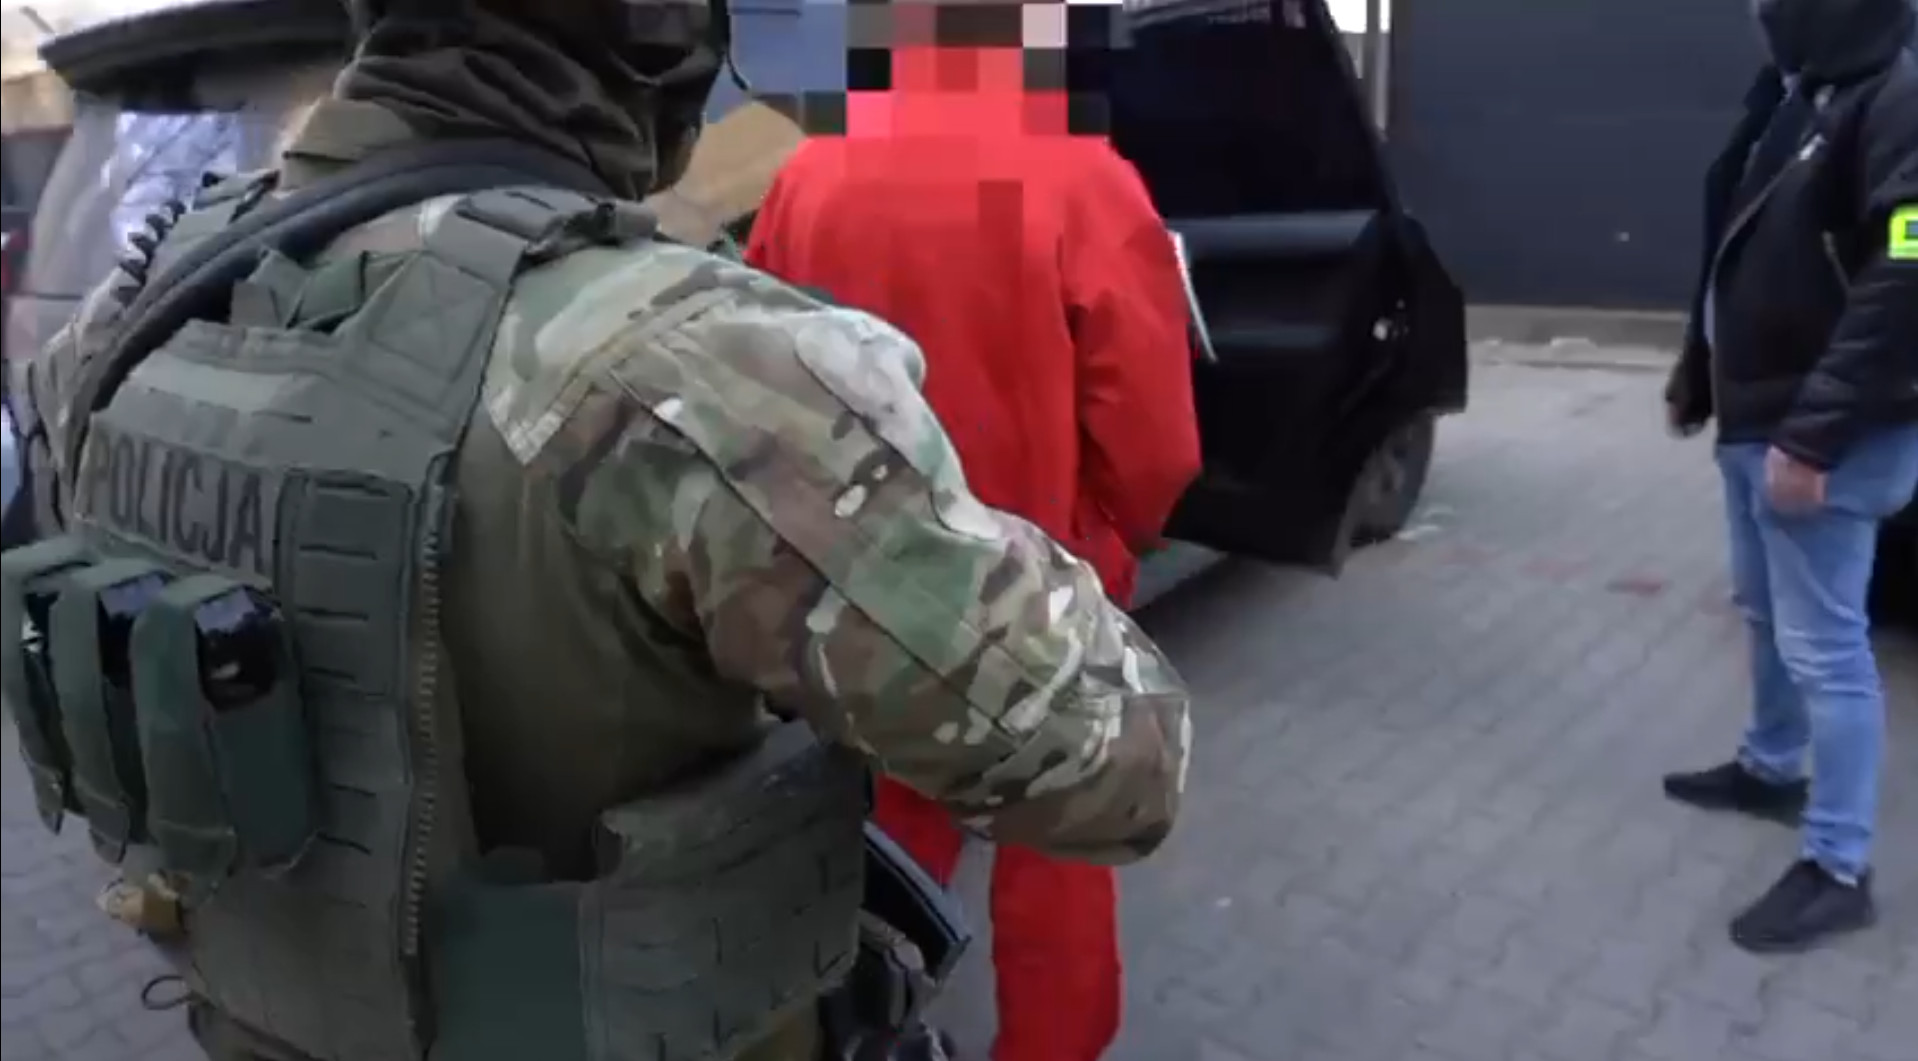
There have been dozens of NATO citizens killed by the Russian government.


IMG_4893.png

Really the only direct actions of Western retribution occurred by US DoD and IC during Trump 45 Administration.
They were also what I would consider periphery incidents, limited to Africa, Ukraine and other contested areas where Russian forces could be targeted ‘indirectly’.
 
You claimed that in the event of hostilities that Cross Border Internet Traffic would stop.
There are a lot of ways to get on the internet.
I did claim that. And there aren't lots of ways to get on runet from NATO space. Presently vless works. In case of war they are already prepared to reduce the available bandwidth/IX's to zero. Anyone caught using any sort of tunneling/split-tunneling etc. will be arrested immediately.

If you are aware of additional, stable, methods of maintaining runet access I would be very interested in hearing about them.
 
Back
Top